// case study
Tracing an SSH attacker
Reading auth.log and the registry to trace an SSH brute-force attack on a Linux server.
Context
A digital forensics case study from my previous portfolio.
What I did
- Analysed a Linux server's
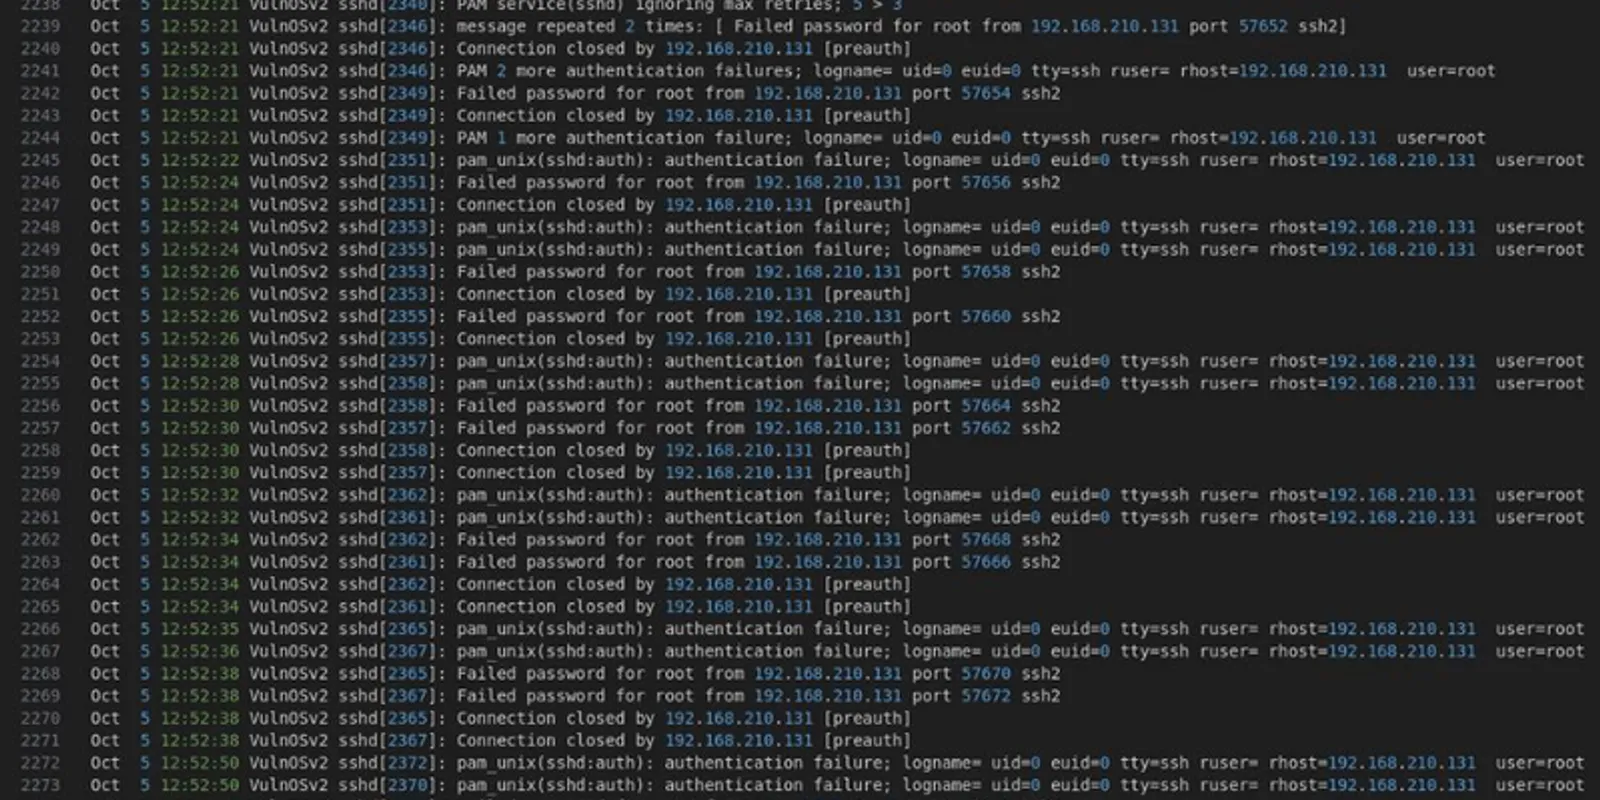
auth.log(VulnOSv2) and found repeated root login attempts from one IP, a sign of SSH brute force. - Reviewed a Windows registry with AccessData Registry Viewer for system context such as time zone and USB devices.