// case study
Network anomaly analysis
Reading packet captures in Wireshark to find suspicious traffic, such as unencrypted Telnet logins.
Context
A networking project from my previous portfolio.
What I did
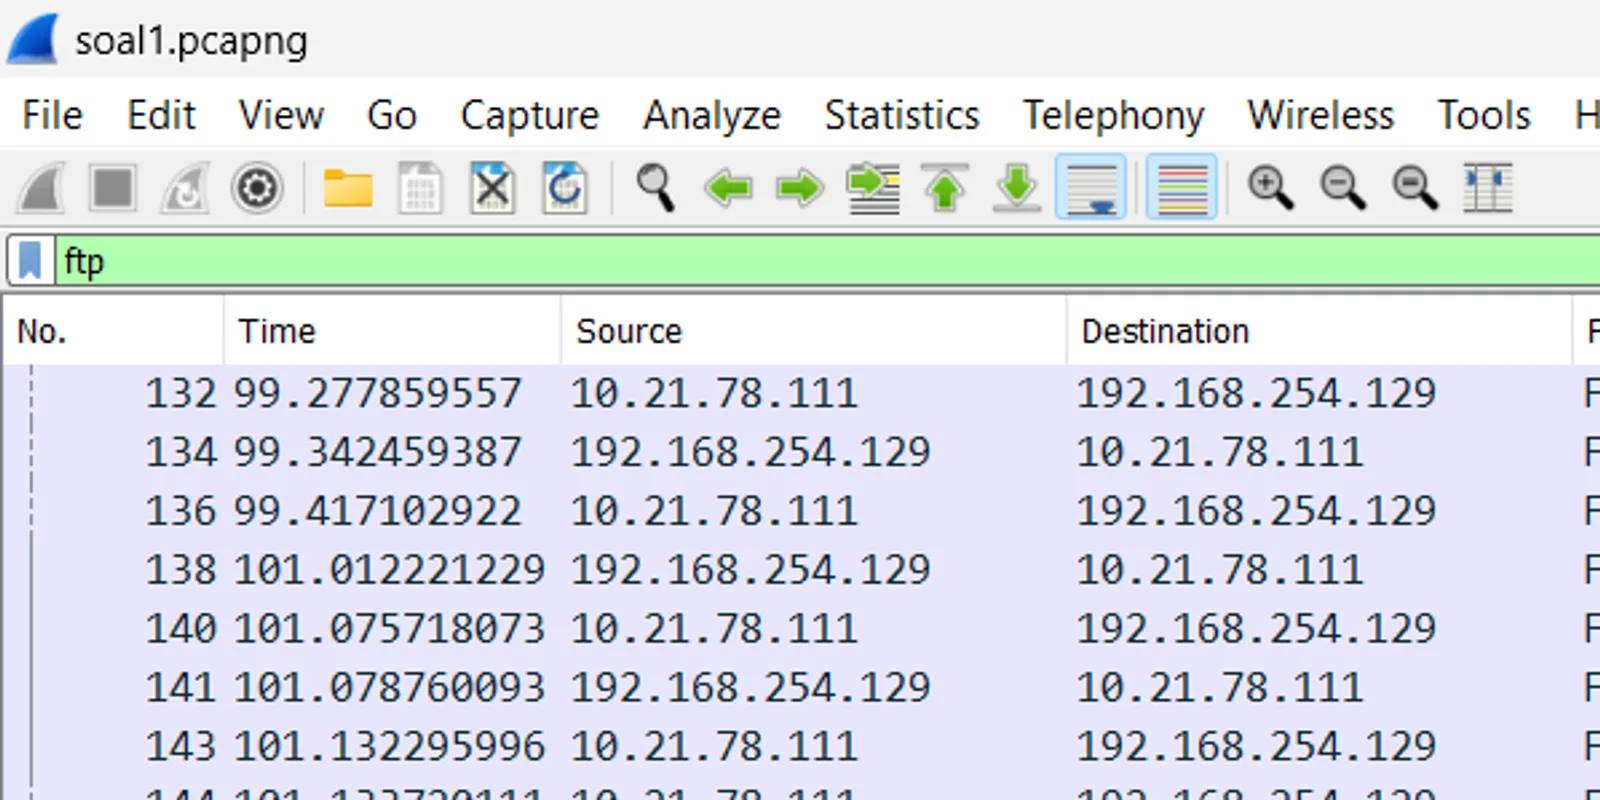
- Filtered traffic in Wireshark, e.g.
ftportcp.stream eq 2, to follow a single session. - Found credentials sent in cleartext over Telnet and traced unusual SYN/ACK/FIN packets.
- Wrote up findings per question from the
.pcapngfiles.