// case study
Uncovering a smuggler
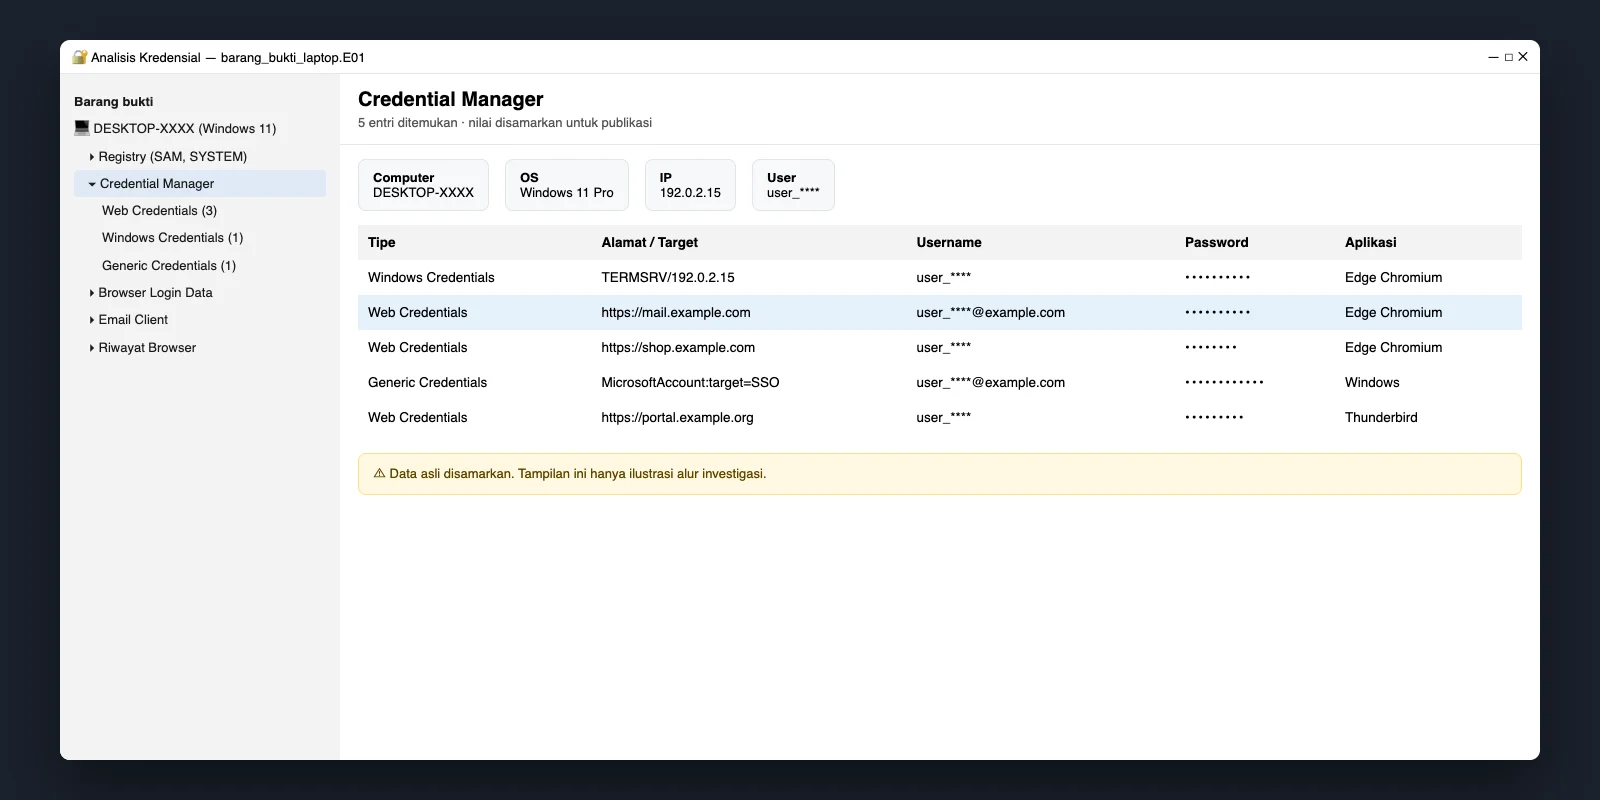
Investigating Windows artifacts to uncover accounts and saved logins on a suspect's device.
Context
A digital forensics case study from my previous portfolio.
What I did
- Extracted system information from the suspect's device (computer name, OS, IP).
- Found the URLs, usernames, and passwords saved in the browser and email client.